Everything in the right hands.
Analyze, prioritize, and triage to make the most out of the opportunities.
Turn your underwriting guidelines into a living risk framework focused on generating more business with sensible prioritization and alignment.

The end of first-in, first-out.
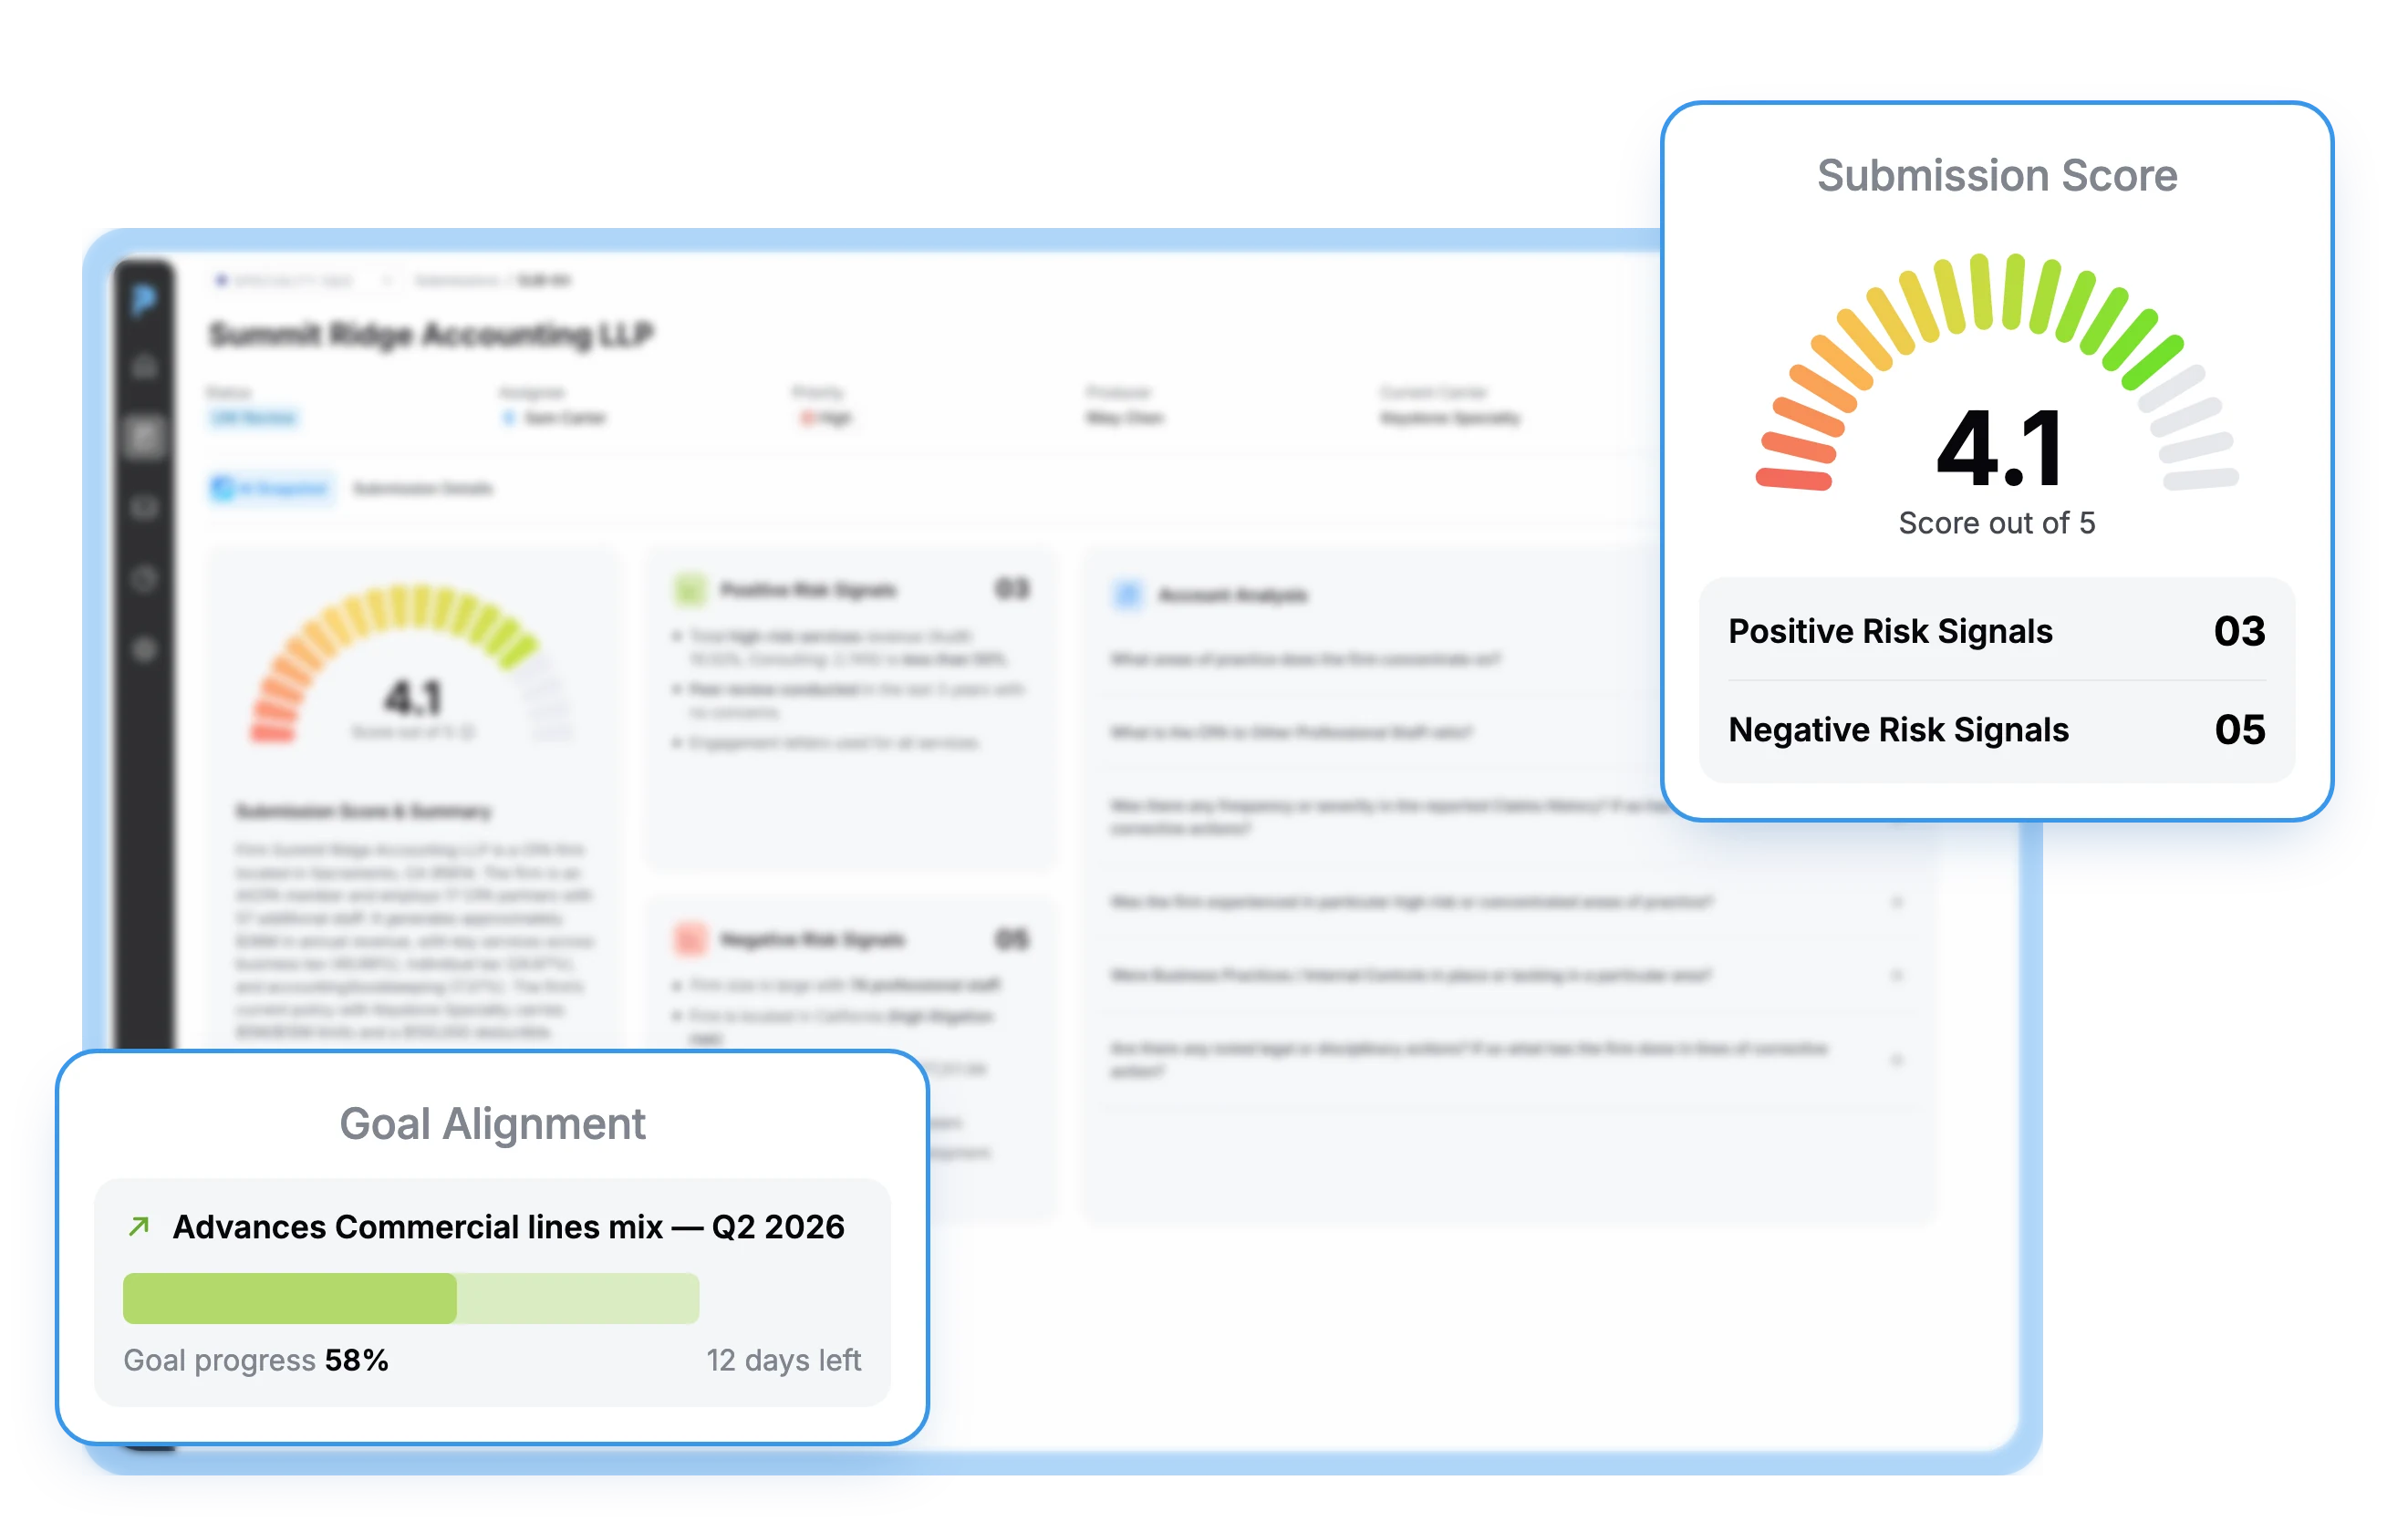
Make the best-fit risks reach the right desk based on appetite, fit, expertise, and authority, before anyone opens the file.
Guideline-driven scoring to eliminate statistical guesswork
Convert your underwriting guidelines into a transparent risk framework with defined factor groups, sub-factors, and weights.
Evaluate every dimension of the file: loss runs, supplements, ACORDs, and government-source data, among other sources.
Set hard-decline factors that drop a submission's score to zero, no exceptions.
Run distinct models by program, LOB, or team, each tuned to its own appetite.
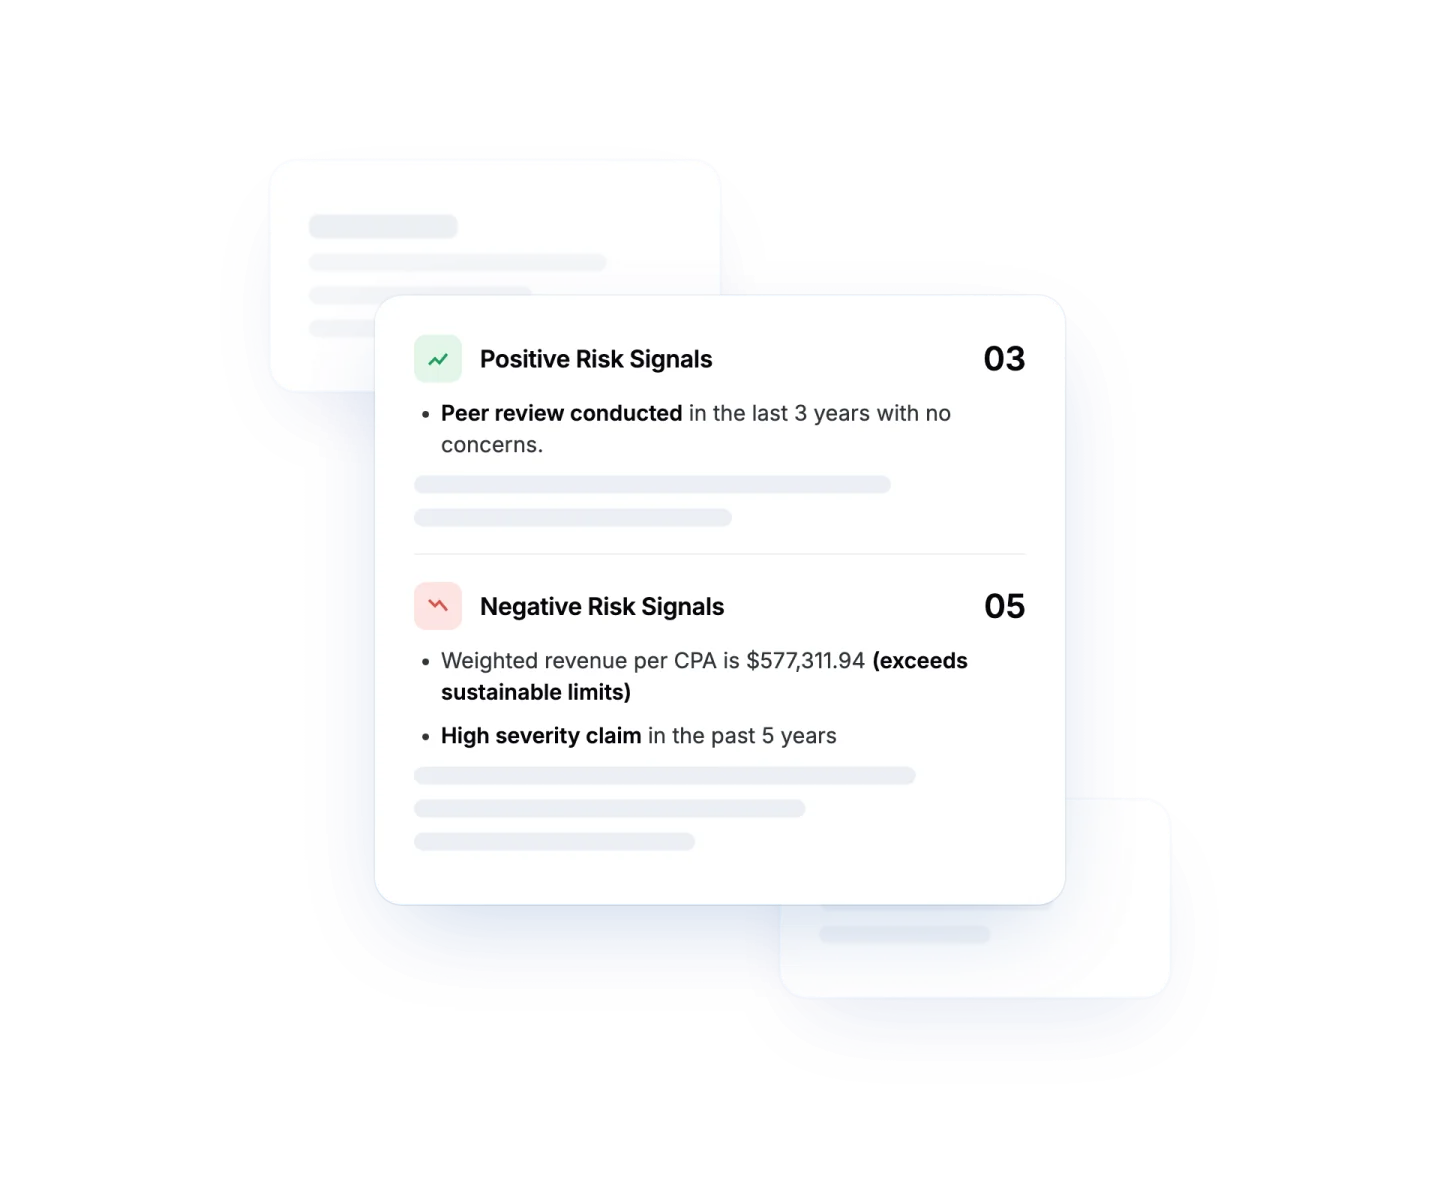
Explainable scores, signal by signal
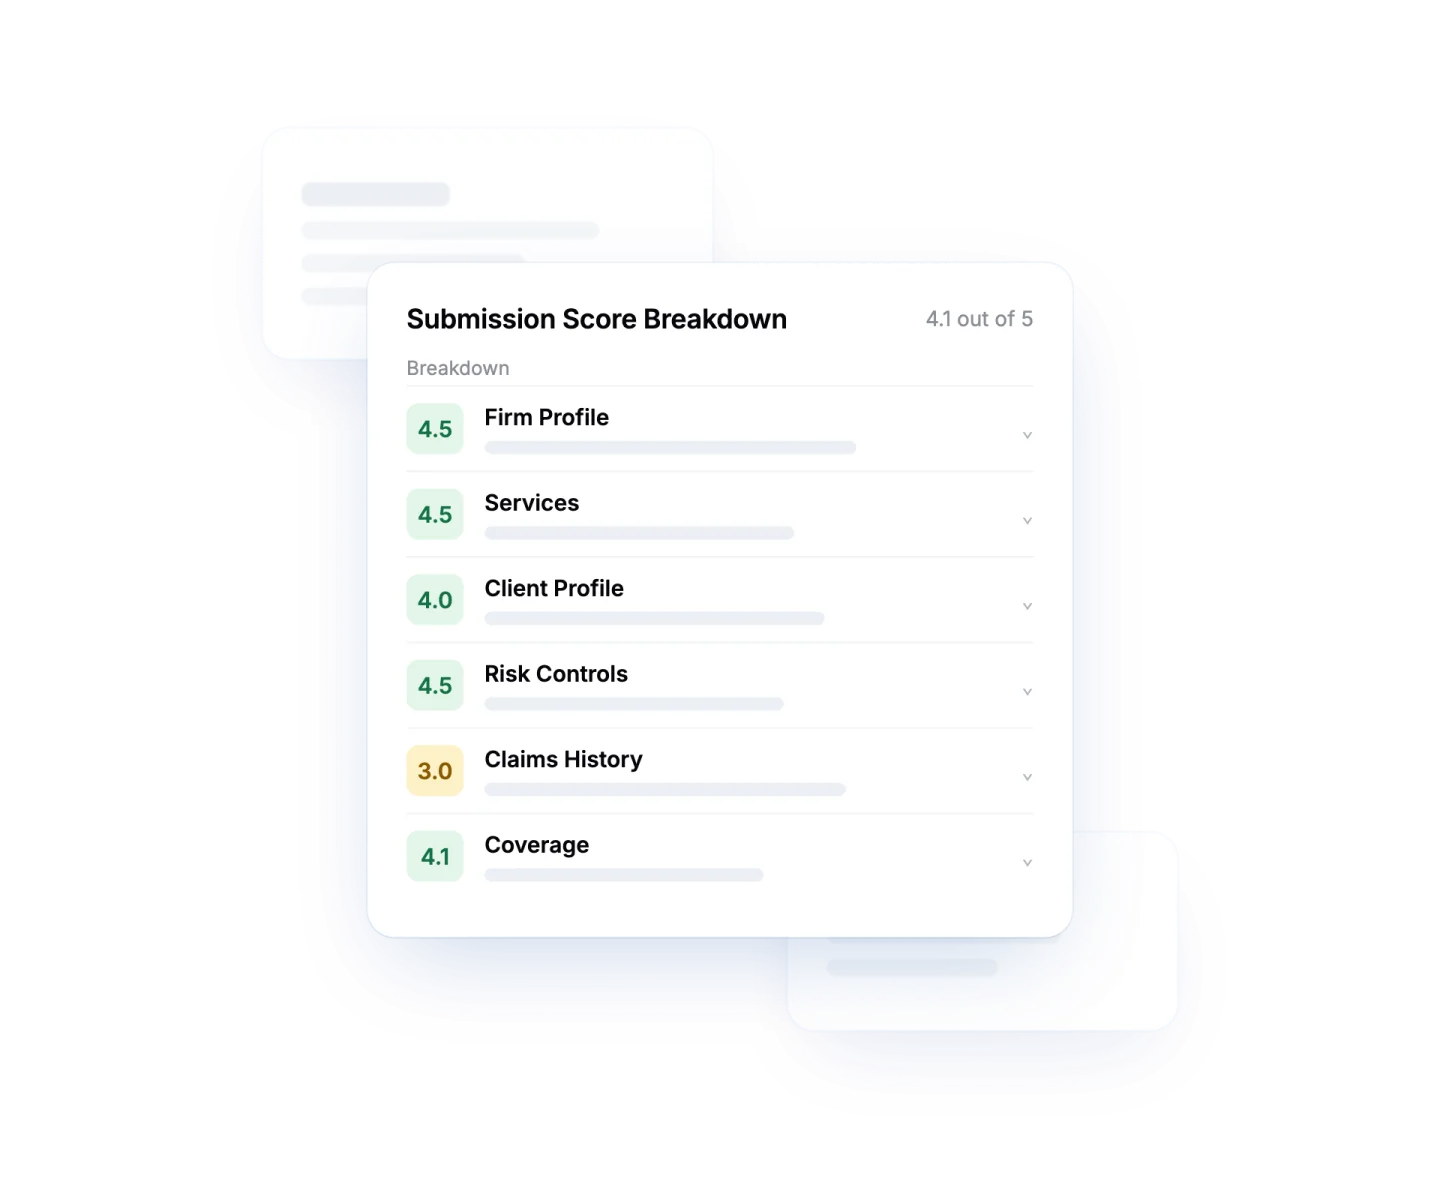
Show underwriters exactly which guideline-driven factors lifted or lowered each score.
Click into any signal to see its source, straight down to the document or data point.
Surface overall positive and negative risk indicators drawn from your own guidelines.
Defend any score to a referral committee, an auditor, or a regulator.
Prioritization aligned to appetite, not time of arrival
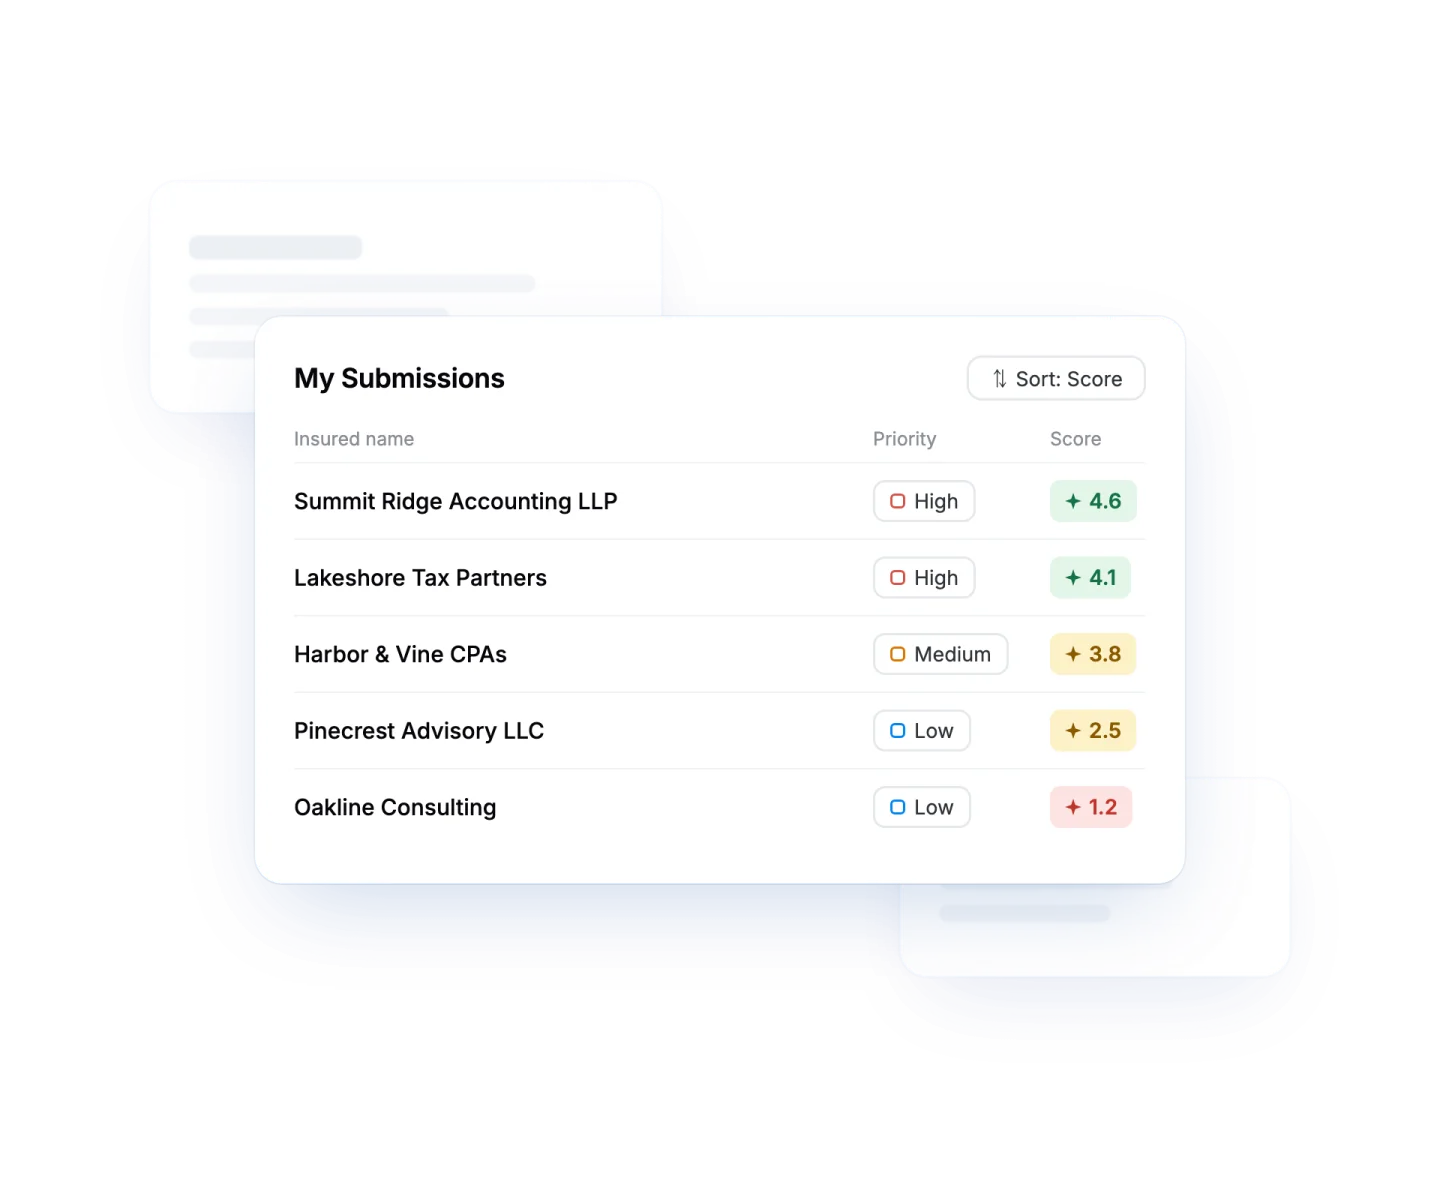
Rank the queue by fit with your guidelines, not by timestamp.
Feed scored metadata into routing or build your own ranking and queues.
See portfolio-level risk distribution, clusters, outliers, and red-flag segments.
An explainable layer your actuaries can interrogate
Start scoring on day one of go-live, with calibration continuing as decisions flow.
Complement internal models by validating and calibrating them with a transparent second read.
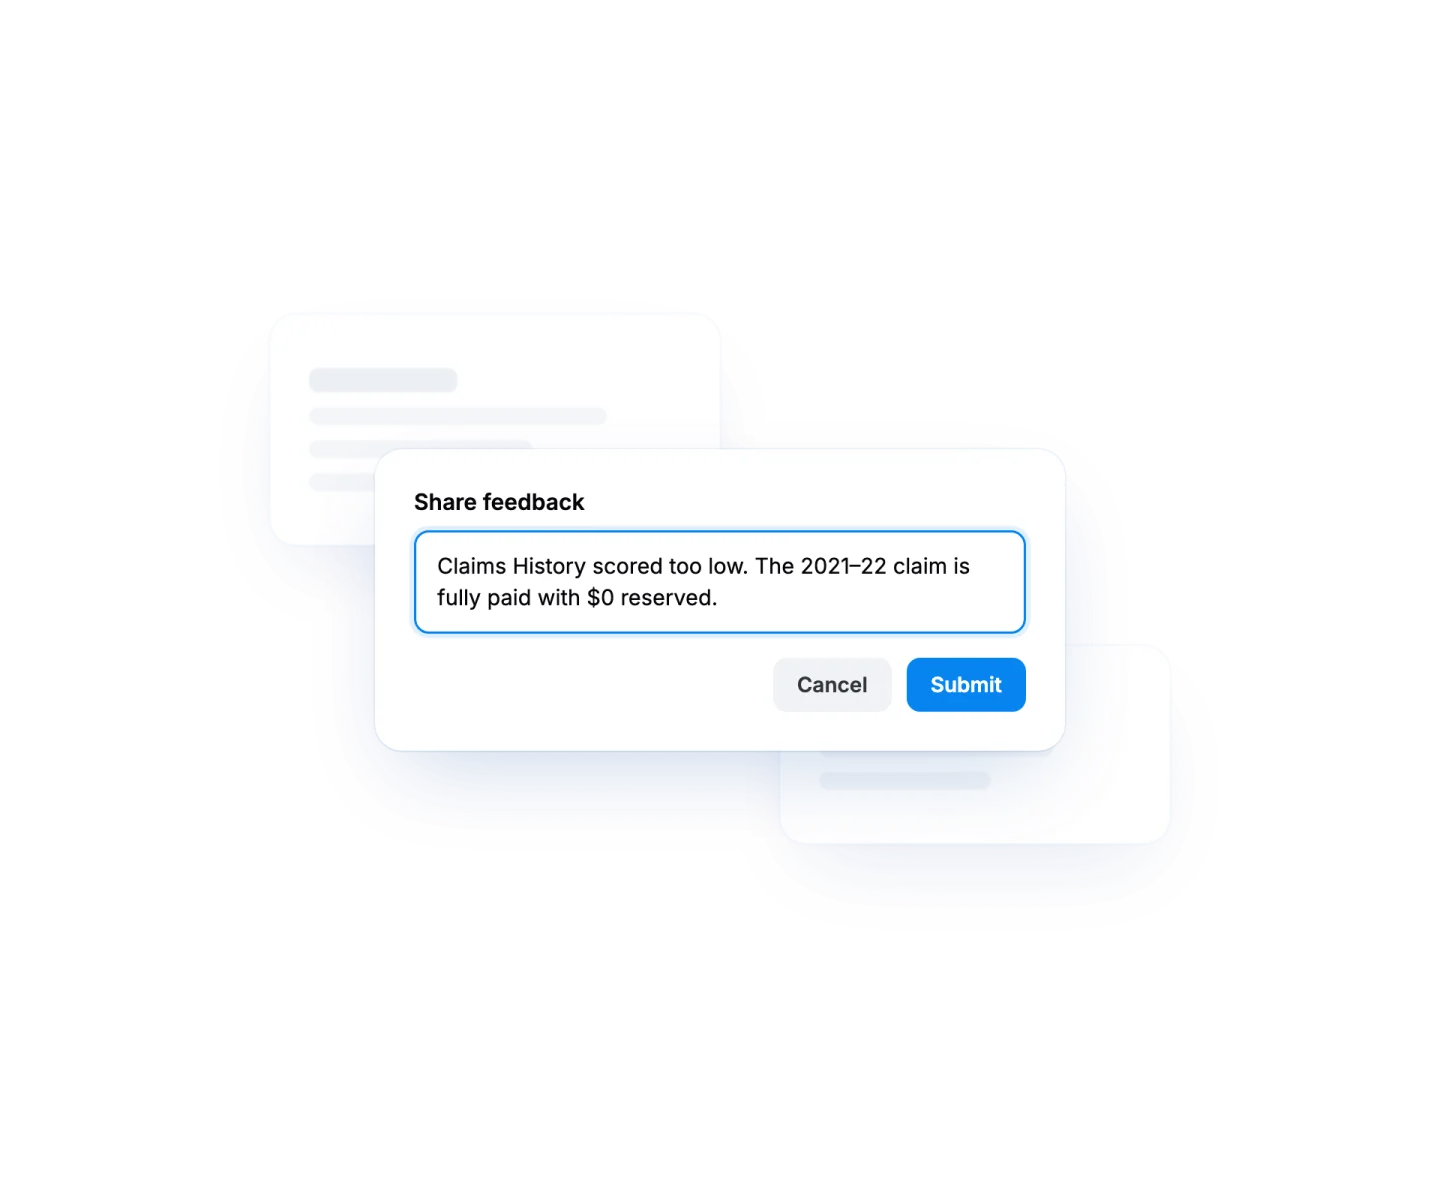
Let underwriters override scores and log structured feedback on misinterpreted factors.
Learn from downstream decisions even in headless deployments.
Give leadership the power to audit and update scoring logic anytime, without engineering.

Increase in
hit ratio

Underwriter throughput

Reduction in
quote time
Ironclad Data Security
Our commitment to data integrity is paramount, and we take pride in meticulously protecting your invaluable information. All customer data is housed in the US AWS regions on SOC 2 Type II and ISO 27001 certified infrastructure, with security controls aligned to NIST SP 800-53 Rev. 5 and CSA CCM v4. We encrypt data at rest with AES 256 through AWS KMS and in transit with TLS 1.2 or higher, enforce least privilege through SAML 2.0 and OIDC single sign-on with role based access controls, and keep every client on a dedicated data and AI stack. Data retention, right to erasure, and PII redaction are supported, audit logging produces immutable evidence trails, and backups and disaster recovery runbooks are tested regularly, so you move fast with absolute confidence.



Request a detailed walkthrough